
Document preview vs read only editor: which view does your workflow need?
Compare viewing workflows by data path, collaboration context, and permission requirements rather than the appearance of the toolbar.
Read storyA document surface must never become a second authorization system. These field notes cover permission-preserving integration, privacy reviews, and the evidence that satisfies a security review.
49 articles · Security + Access control + Data privacy
Compare viewing workflows by data path, collaboration context, and permission requirements rather than the appearance of the toolbar.
Read story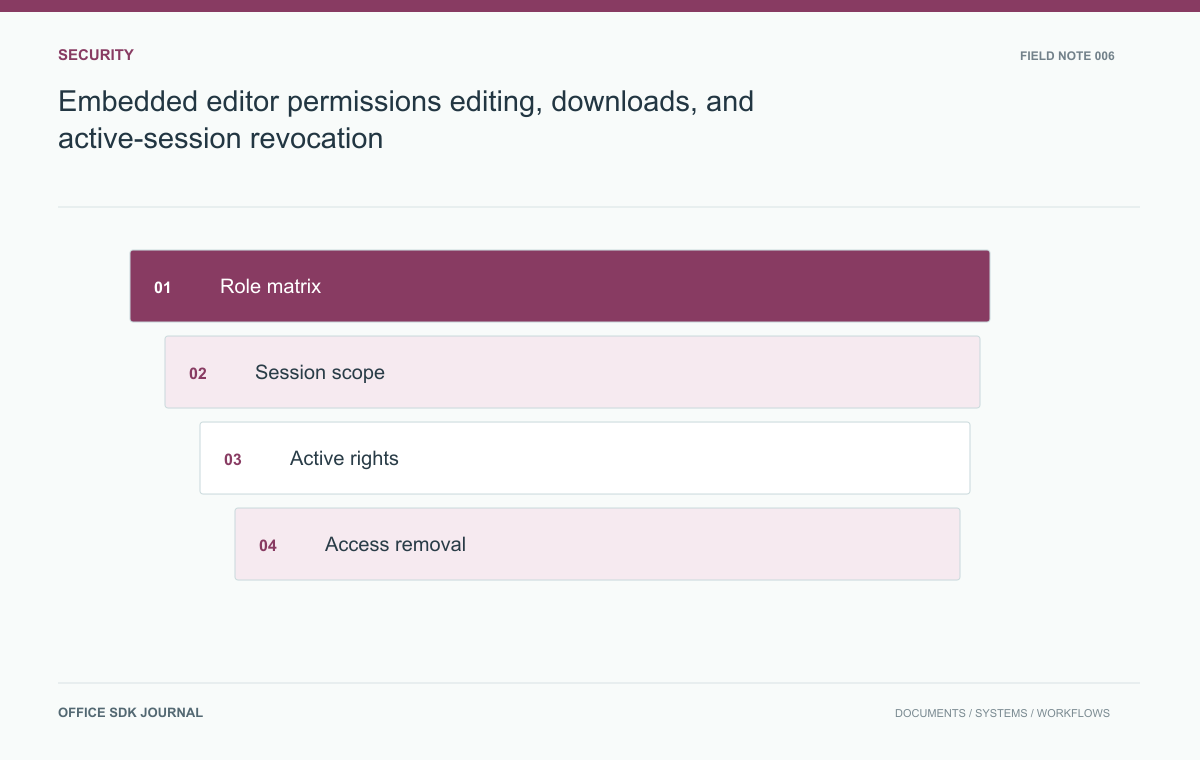
Plan authorization checks for session creation, active editing, exports, and revocation across an embedded document workflow.
Read story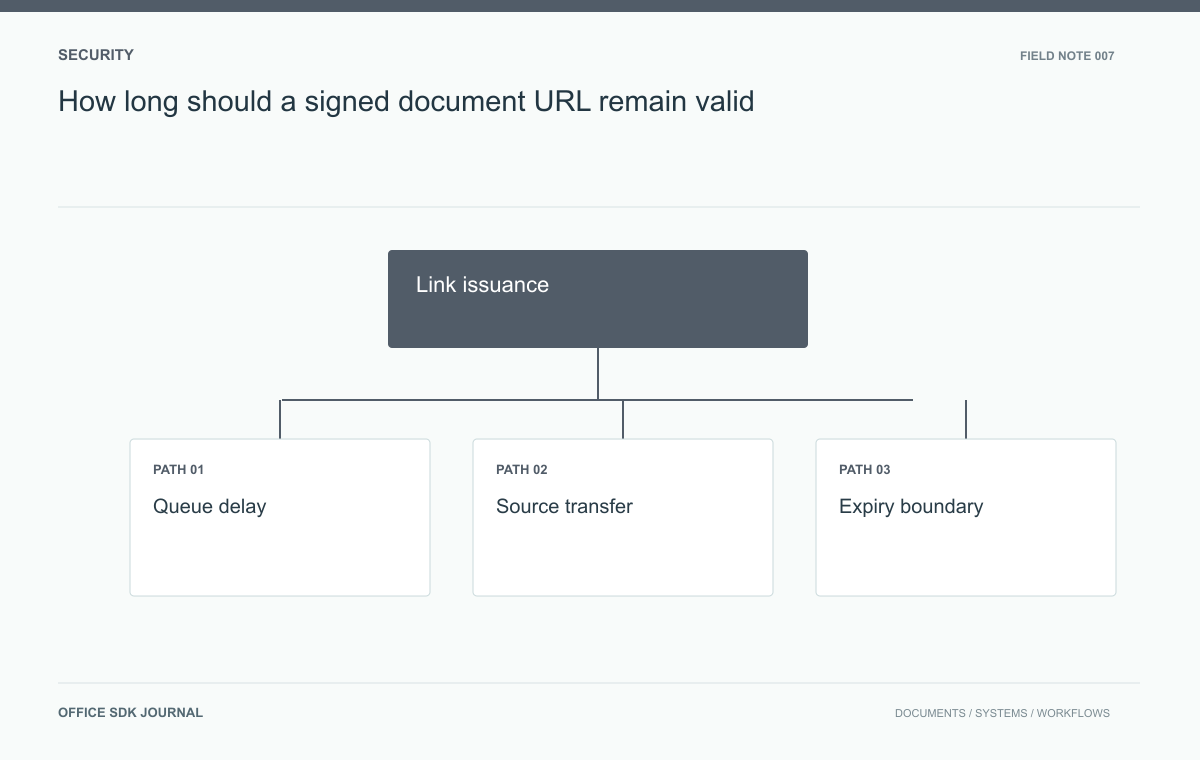
Choose link expiry from queueing, download, and retry behavior while limiting the exposure of temporary document access.
Read story
Structure uploads so validation, scanning, and release happen before untrusted files reach shared document workflows.
Read story
Collect the environment, operation sequence, and smallest useful fixture so document failures can be reproduced safely and precisely.
Read story
Identify separate session lifetimes and verify what logout, account switching, and access revocation actually terminate.
Read story
Use a narrow, tested content security policy for the host page and understand which controls belong to the embedded origin.
Read story
Distinguish cookies, mixed content, cross origin requests, extensions, and engine compatibility when an embedded editor fails to load.
Read story
Set explicit extraction rules for visible text, comments, hidden sheets, formulas, images, and embedded objects.
Read story
Reduce unnecessary document exposure with task scoped selection, permission checks, and explicit handling of derived content.
Read story
Attach useful provenance to generated answers so readers can inspect evidence, detect stale sources, and review uncertainty.
Read story
Separate approved template versions from created documents, with clear ownership, change review, and retirement behavior.
Read story
Track every source document through transfer, transformation, permission mapping, and final acceptance with an auditable manifest.
Read story
Turn document deletion into a tracked lifecycle with clear user visibility, retention rules, and cleanup of derived copies.
Read story
Choose preview, editing, conversion, or download paths using validated content type and task requirements, with clear fallback behavior.
Read story
Record business actions, version relationships, and authorization context without confusing audit history with raw application logs.
Read story
Build a replacement inventory around records, permissions, workflows, and recovery obligations.
Read story
Separate cryptographic assurances from the search, recovery, sharing, and administration work a team needs.
Read story
Prepare a manual knowledge migration with explicit handling for attachments, links, permissions, and unsupported content.
Read story
Use bounded pilots, access evidence, and operational ownership to introduce collaborative document workflows in banking.
Read story
Connect matter membership, review versions, external exchange, and preservation duties in one document workflow.
Read story
Define working drafts, official records, access decisions, and accessible publication in public sector workflows.
Read story
Inventory effective permissions, resolve group mappings, and verify access after a staged drive migration.
Read story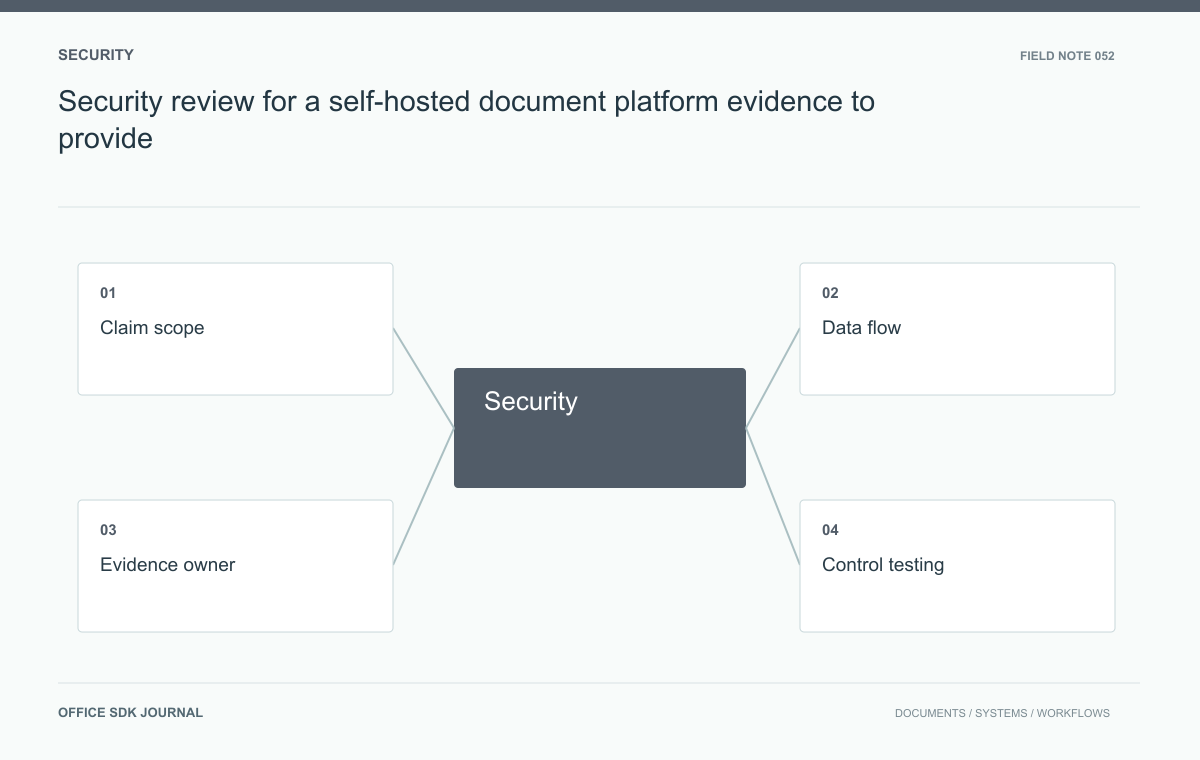
Turn review questions into scoped claims backed by architecture, configuration, operational evidence, and named owners.
Read story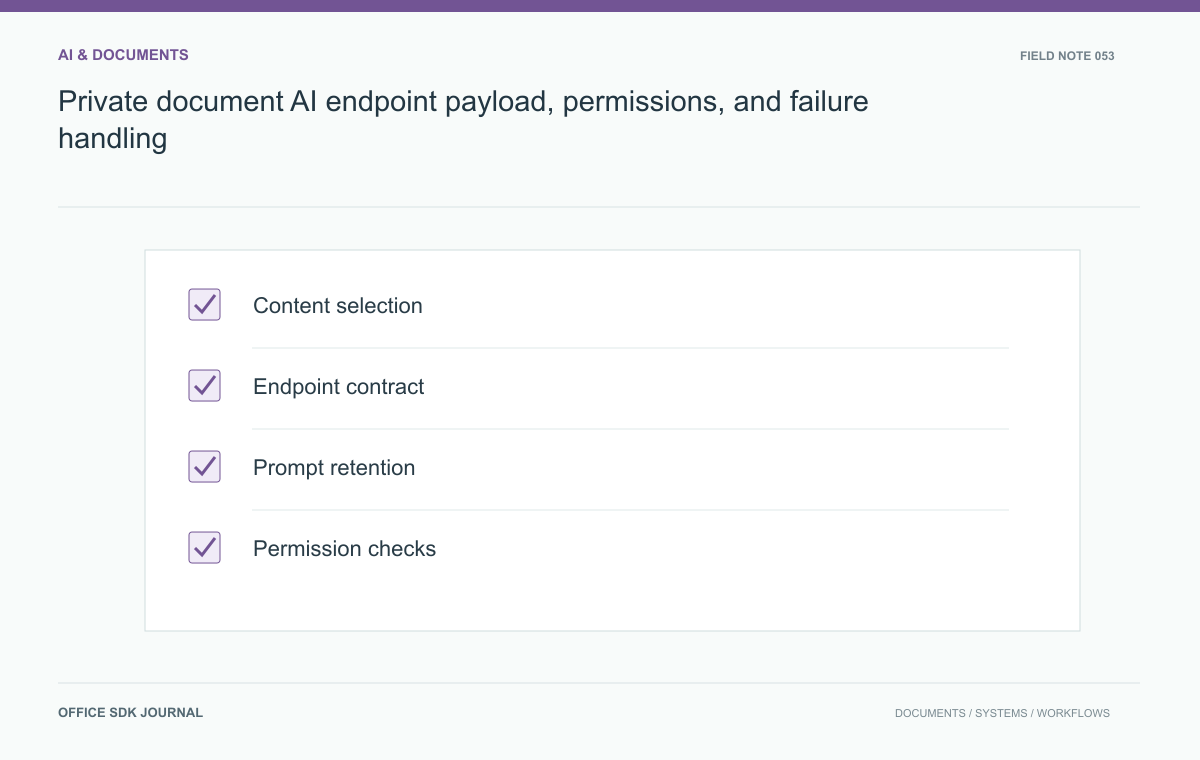
Define content selection, authentication, model compatibility, logging, and failure behavior before enabling a private AI endpoint.
Read story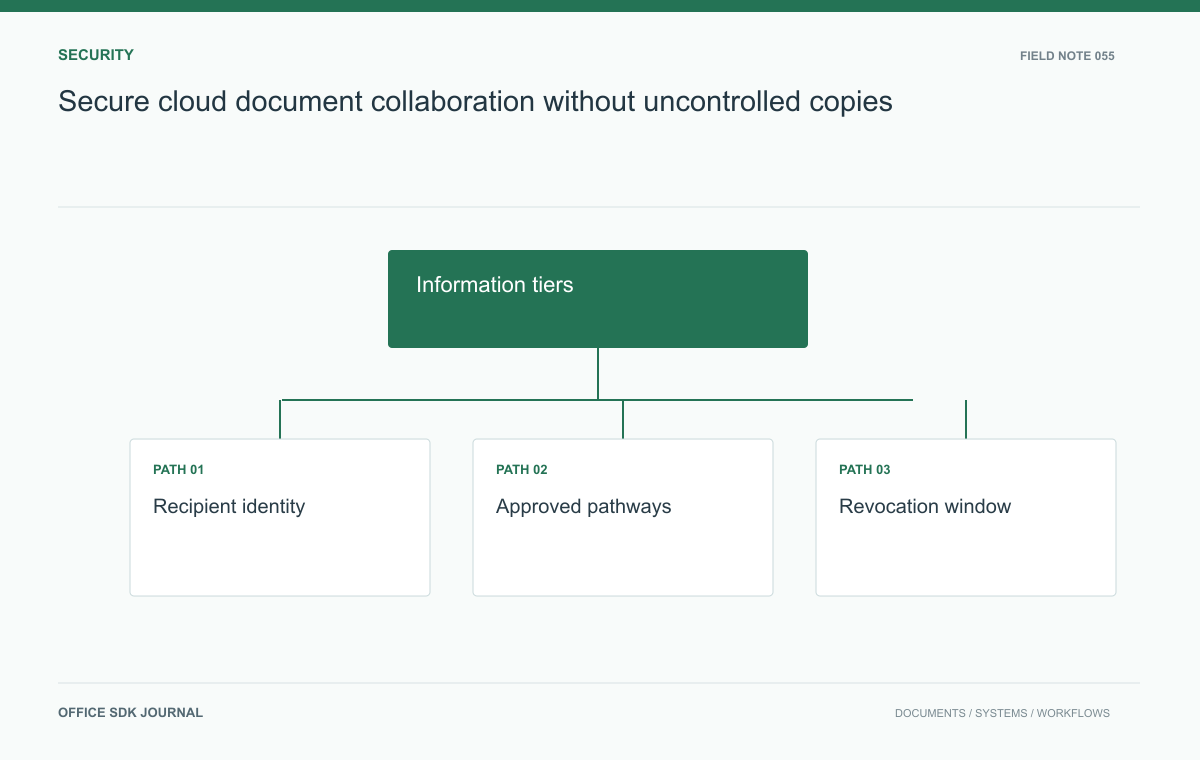
Connect information classification, recipient identity, practical access rules, and observable revocation in cloud collaboration.
Read story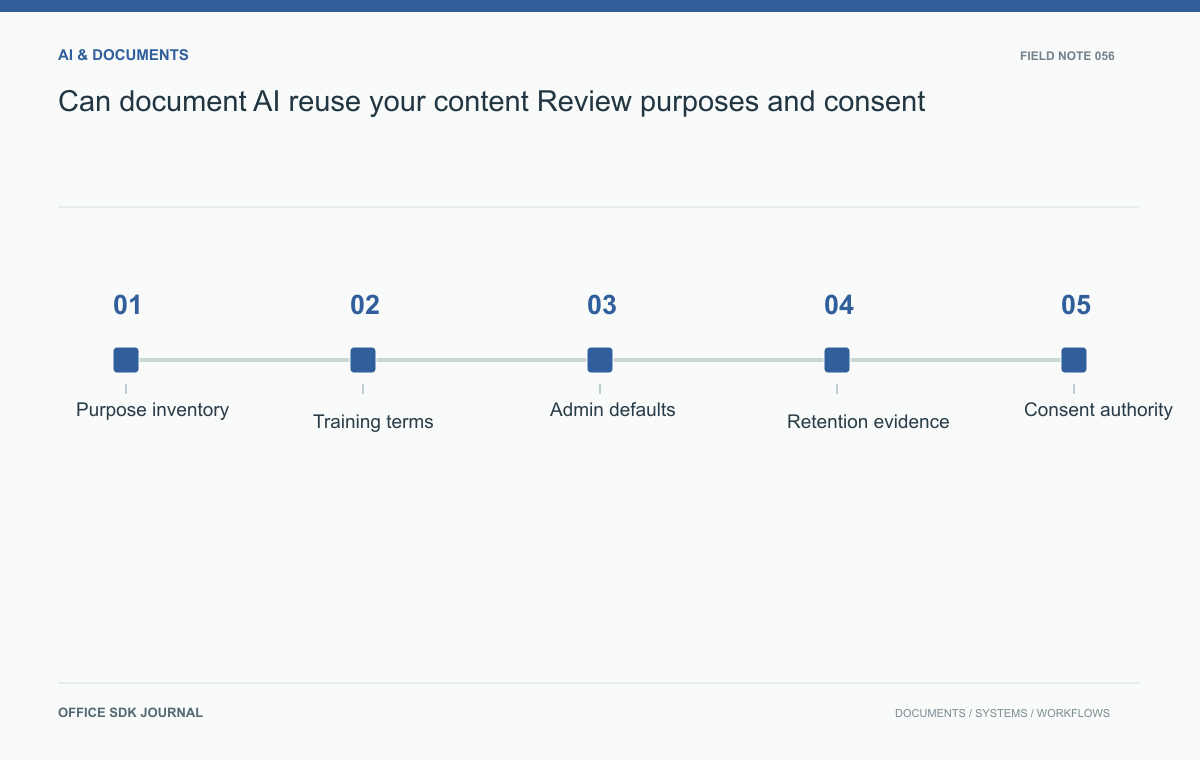
Review inference, training, evaluation, logging, and consent as distinct uses of document information.
Read story
Select complementary testing, deployment, monitoring, and incident resources using contract risk and accountable evidence.
Read story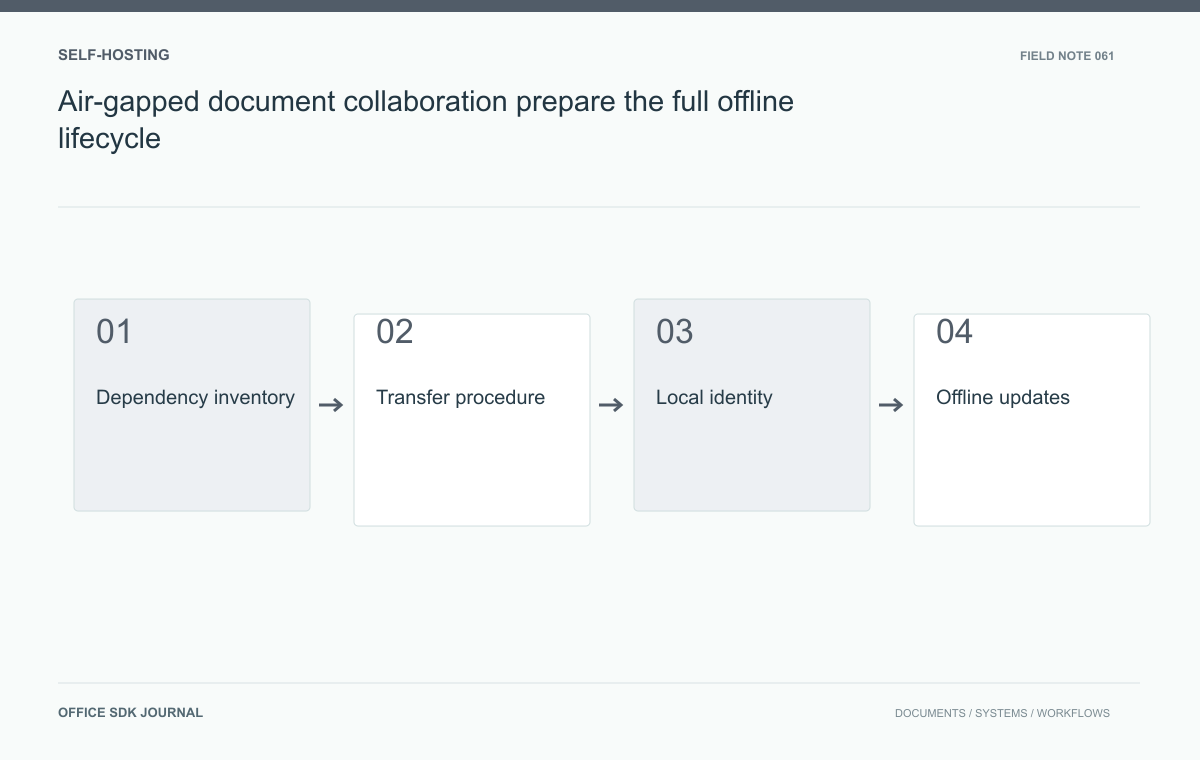
Prepare installation, identity, fonts, updates, support, and recovery for a genuinely disconnected document environment.
Read story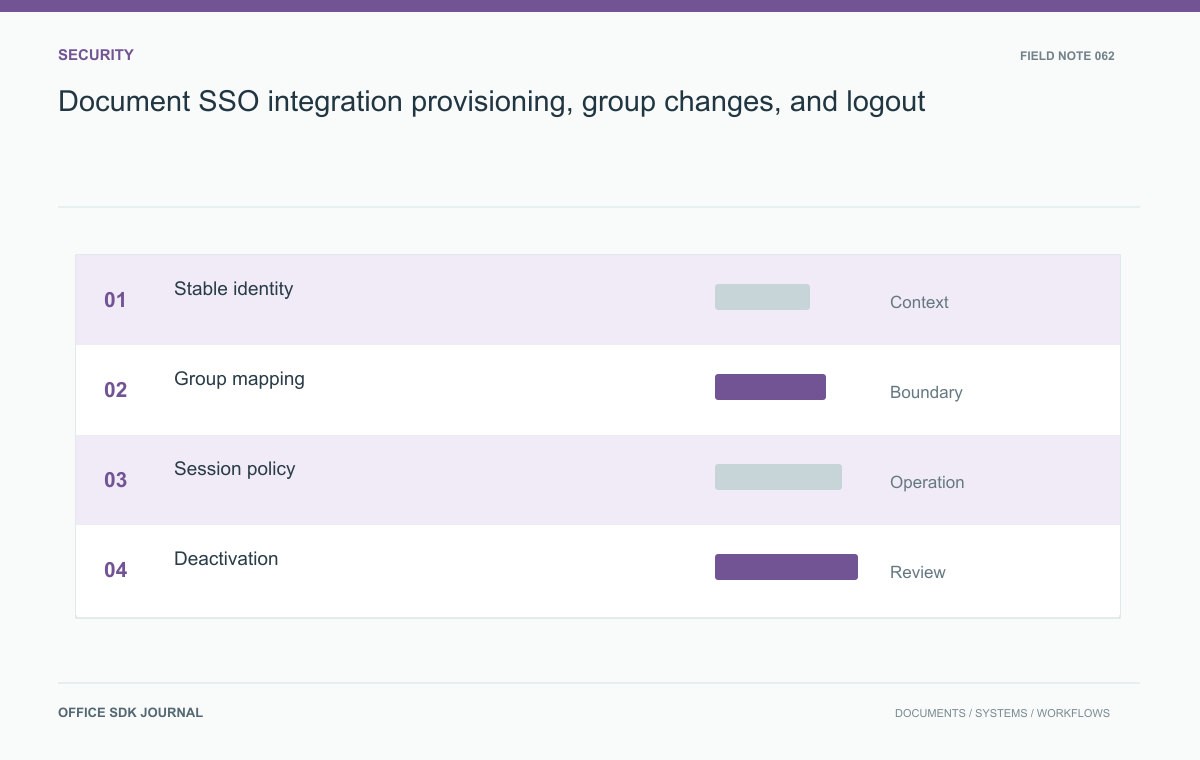
Connect login, provisioning, group mapping, deactivation, and recovery instead of stopping at a successful redirect.
Read story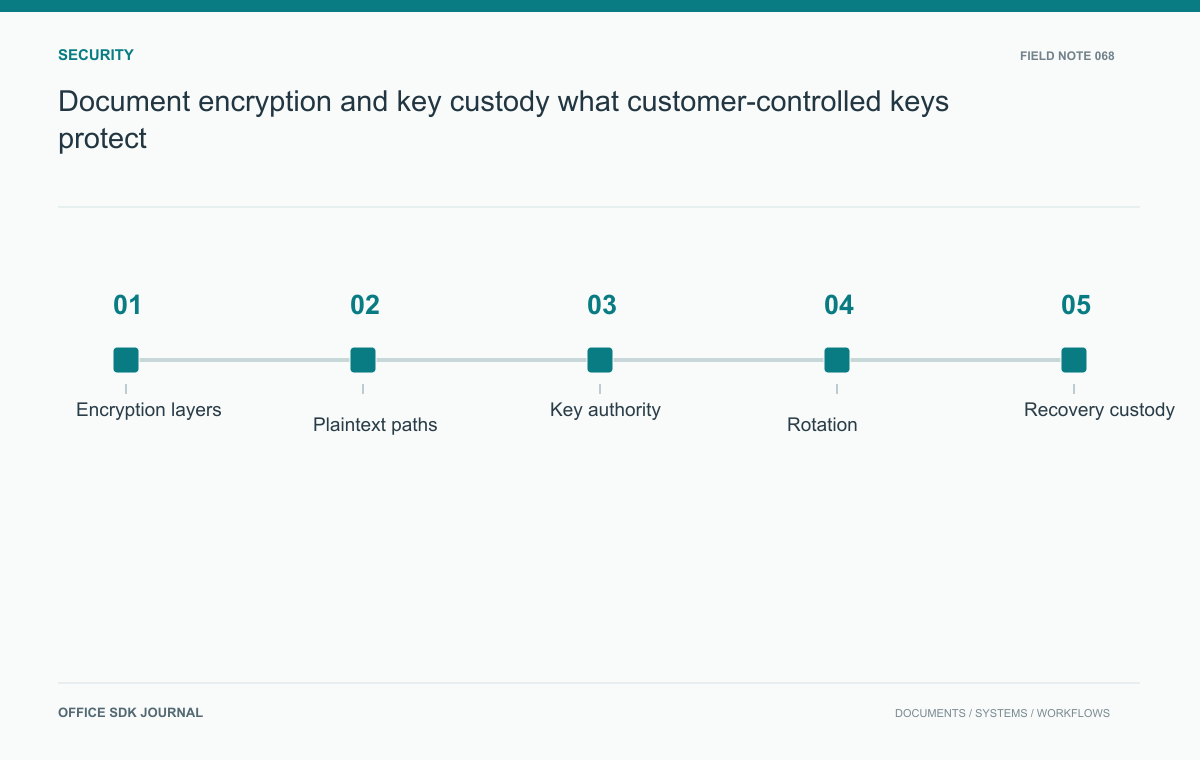
Map encryption layers, key authority, rotation, recovery, and the components that still handle readable content.
Read story
Find external access risks by testing recipient boundaries, version scope, attachments, revocation, and ownership.
Read story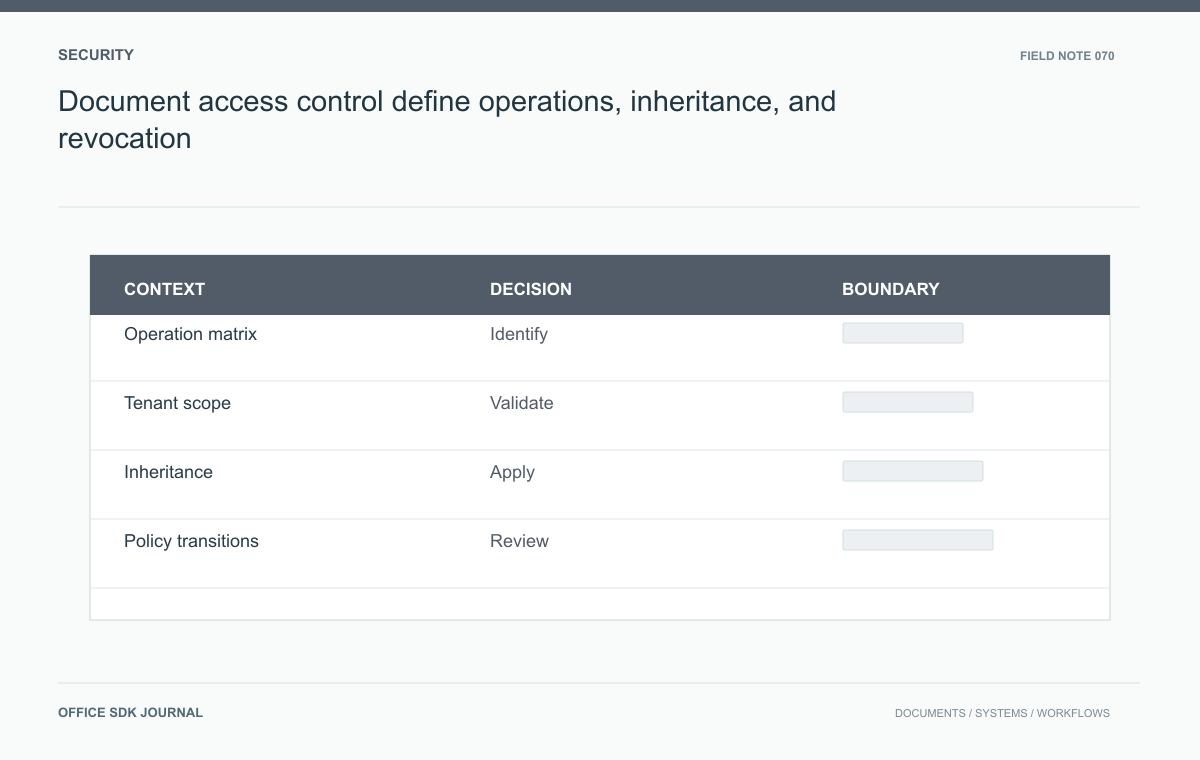
Model allowed actions, inheritance, tenant scope, policy changes, and direct endpoint enforcement with testable decisions.
Read story
Connect counsel's scope, technical preservation, custodians, verification, and controlled release of a document hold.
Read story
Define record classes, retention triggers, exceptions, technical mapping, and evidence of approved deletion.
Read story
Map storage, processing, backups, support access, telemetry, and AI destinations against the actual residency requirement.
Read story
A practical evidence map for access reviews, sharing exceptions, recovery tests, and corrective actions.
Read story
How to assemble complete access and change populations, defensible samples, and honest exception records.
Read story
A workflow assessment for PHI, business associate arrangements, secondary copies, and clinical continuity.
Read story
Locate personal data in drafts, comments, exports, indexes, and backups before implementing retention or rights decisions.
Read story
Protect financial document workflows with version-bound decisions, controlled external access, and recoverable evidence.
Read story
Limit agent reads and tools, test hostile document content, and guard consequential publication.
Read story
Move documents without losing unfinished work or the context of links, permissions, and submitted versions.
Read story
Separate storage residency, processing locations, legal access, and operational control in a document workflow.
Read story
Write a responsibility model for infrastructure, document state, privileged access, maintenance, and recovery.
Read story
Create a work contract for agents that coordinate document, workbook, and presentation tasks.
Read story
Prove the offline boundary and validate local outputs under ordinary operation, failure, and maintenance.
Read story
Preserve document meaning and evidence through local parsing, context selection, inference, and rendering.
Read story
Assess safe code, native interfaces, parser limits, correctness, deployment, and maintenance without language-based performance claims.
Read story